Plugin4Shell and Claude Code 2.1.179: Securing AI Coding Agent Plugins, Parallel Agents and Safari's MCP Server
Plugin4Shell let attackers bypass SHA-pinned plugins in Claude Code, Codex, Copilot and Gemini CLI. Which versions fix it, how Claude Code Projects now runs parallel cloud sessions, what Safari 27's MCP server exposes, and a practical security checklist for coding agents.
In mid-September 2026, several developments changed how teams should manage AI coding agents. Security firm Air Security disclosed Plugin4Shell, a flaw that let attackers bypass the SHA pinning that agent plugin marketplaces rely on. Anthropic redesigned Claude Code Projects to split one goal across parallel cloud sessions. Apple shipped an MCP server in Safari 27 so agents can inspect real browser windows. And GitLab and Applitools added agent tools with approval controls. The short version: update Claude Code to 2.1.179 or later and Codex to 0.146 or later, review how plugins are approved, and decide where parallel and browser-driving agents are allowed to run. This guide explains each change and ends with a checklist.
Plugin4Shell: what the vulnerability is
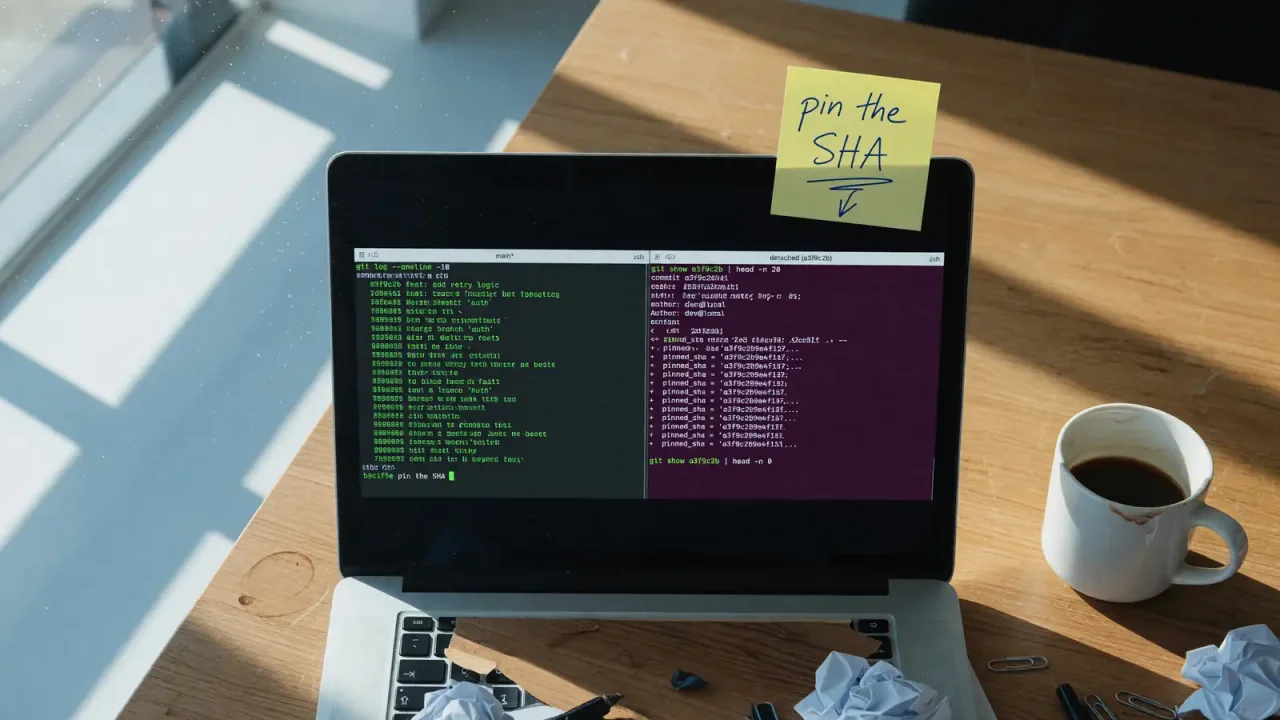
Agent plugin marketplaces typically protect users by pinning each plugin to a reviewed commit SHA. The idea is that code is reviewed once at a specific commit and that exact commit is what gets installed. According to Air Security’s disclosure, published September 17, 2026, the agents checked out the pinned commit but did not verify where the checkout actually landed.
For Claude Code, Codex and GitHub Copilot, an attacker who controls a plugin’s repository can create a branch named exactly like the 40-character pinned SHA. When the agent runs git checkout <sha>, git resolves the branch name instead of the commit, so the attacker’s code is installed while the pin appears to be honoured. Gemini CLI had a different variant in which the pinned ref was fetched but never checked out.
Air Security describes the issue as zero-click remote code execution because Claude Code and Codex update installed plugins in the background by default. If the pinned commit is swapped upstream, a plugin the user already trusts can be replaced without any prompt.
The GitHub security advisory for Claude Code (CVE-2026-86063, rated high severity) confirms the details: affected versions are below 2.1.179, the fix verifies that the resulting HEAD matches the pinned SHA, and users on standard auto-update have already received it. The advisory notes exploitation required a malicious plugin source on a git host that permits SHA-shaped branch names.
Fix status by agent
| Agent | Status according to Air Security and the advisory |
|---|---|
| Claude Code / Claude Desktop | Fixed in 2.1.179 (CVE-2026-86063) |
| OpenAI Codex | Fixed in 0.146 |
| GitHub Copilot (VS Code) | Fixed; Air’s November update says VS Code 1.136.0 checks that the checked-out commit matches the pinned SHA |
| Gemini CLI | Not fixed; Google has deprecated it and recommends migrating to Antigravity |
An earlier version of this article said Copilot had not been patched, based on reporting at the time. Air Security’s updated disclosure states Microsoft has since fixed it.
Why it matters beyond one bug
Many internal plugin review processes assume that a pinned SHA is a strong guarantee. Plugin4Shell shows that the guarantee depends on the client verifying the result. Air recommends that any tool installing pinned code check the resolved HEAD, not just the ref it requested, for example with a check like test "$(git rev-parse HEAD)" = "<pinned-sha>". Teams building their own agent tooling or plugin installers should apply the same rule.
Claude Code Projects: parallel cloud sessions
The Pondero newsletter reported that Anthropic shipped a redesign of Claude Code Projects on September 17 to a portion of Pro and Max subscribers. Given a goal across multiple repositories, Projects opens a cloud thread for each sub-task, such as migrating callers, running tests and filing pull requests, and runs them simultaneously. Each worker is a full cloud session on its own branch.
Two practical consequences follow. First, usage scales with the number of threads, so a coordinator that opens several sessions consumes limits faster; Pondero’s earlier brief noted that per-project usage tracking shipped in the same release. Second, the feature runs in the cloud, so organisations with policies against cloud-hosted agents need to review it before enabling. We covered a similar move in Cursor’s cloud agents running in Cloudflare sandboxes.
Parallel agents work best when each has its own branch or worktree and when tasks are independent. Running several agents against one shared working tree produces conflicts that are hard to review. For general patterns, see our overview of multi-agent AI frameworks.
Safari 27’s MCP server
Apple introduced the Safari MCP server in Safari 27 and Safari Technology Preview 247. Built on safaridriver, it lets any MCP-compatible client connect to a Safari window without an extension. To enable it, turn on “Show features for web developers” in Safari’s Advanced settings, then “Allow remote automation and external agents” in Developer settings, and configure the client to run /usr/bin/safaridriver with the --mcp argument.
Available tools include reading console messages, listing and inspecting network requests, extracting page content as markdown or HTML, evaluating JavaScript, taking screenshots, and performing interactions such as clicking and typing. WebKit says the server runs entirely on the local machine and makes no network calls of its own, and that it does not have access to AutoFill or other browser activity.
The benefit is clear for Safari-specific layout and compatibility bugs: an agent can see the rendered page, console and network activity instead of relying on a developer’s description. The risk is that an agent can operate a real browser. Use a separate browser profile for agent sessions, keep it away from accounts like email and single sign-on, and test against development or staging sites.
GitLab 19.4: agent writes behind approval
According to the Pondero briefs, GitLab 19.4, released September 17, extended its MCP server so outside clients such as Claude Code, Cursor and VS Code can work with pipelines, merge requests, issues, repository commits and vulnerability triage. Tools include retrieving a failed job’s trace, leaving batched line-level review comments and accepting a merge request once checks pass. Read-only tools default to “Always Allow” and write or delete tools default to “Always Ask”, configurable per tool in group and project settings. Administrators should confirm that write tools have not been switched to Always Allow before issuing tokens to agents.
Applitools: visual checks for agent-written UI
On September 15, Applitools announced Eyes Visual AI MCP Tools in a paid press release. The tools connect its visual testing to Claude Code, Cursor, Copilot and Cline, giving agents visual differences and page-structure snapshots to tie layout shifts to source code. Applitools says agents can perform baseline maintenance, including accepting or rejecting changes and masking dynamic data, and claims this cuts test maintenance overhead by up to 95%. The release also cites Faros AI telemetry showing median pull request review times up five times and production incident risk more than tripling as teams adopt coding agents. These are vendor-reported figures.
The underlying point is reasonable: a model reading code cannot reliably see how a page renders across browsers and devices. Deterministic visual tests, whether from Applitools or an existing screenshot suite, give a more consistent signal. Accepting a new visual baseline is effectively approving a production change, so many teams will want to keep that step with a human even if agents propose the diff.
Security checklist for coding agents
- Check versions. Claude Code 2.1.179 or later, Codex 0.146 or later, VS Code 1.136.0 or later for Copilot. Include CI images and shared developer machines.
- Inventory plugins. List installed agent plugins and their source repositories. Reopen reviews that relied solely on SHA pinning.
- Handle Gemini CLI. Since it will not be patched, avoid marketplace plugins there and plan migration.
- Prefer plugins you control. Fork plugins into repositories your organisation owns where possible.
- Isolate parallel agents. One branch or worktree per agent, with usage limits set before large runs.
- Review cloud features against data policy. Decide which data classes may be used with cloud-hosted agent sessions.
- Separate browser profiles. Give browser-driving agents a dedicated profile with no personal or SSO sessions.
- Keep approvals for writes. Use approval modes such as GitLab’s Always Ask for merges and other write actions.
- Add visual checks. Run visual or screenshot tests on agent-written UI before review.
- Write it down. Put minimum versions, plugin rules and allowed features in a short policy page.
For day-to-day usage tips, see our guide to Claude Code for pair programming.
Our analysis
The September changes share a theme: coding agents are gaining reach, running in parallel in the cloud, driving real browsers and acting on DevOps systems, and each step requires matching controls. Plugin4Shell is the clearest example of a control that looked solid but depended on an unchecked assumption. The fixes are simple to apply for most teams, since auto-update has already delivered them for many Claude Code users, but the lesson is broader. Any security guarantee in an agent workflow should be verified at the point where code actually runs, and approval steps for write actions are worth keeping even as agents become more capable.